One ACME Standard. Three HTTPS Automation Approaches.
Automate SSL/TLS certificate lifecycle management through different deployment architectures, from server-based automation to enterprise gateway deployment and CDN API integration.
ACME Client
Install on Your Web Server
Install an ACME client on your Web server to automate certificate issuance, deployment, and renewal.
A widely adopted approach for environments where server-level installation and configuration are supported.
ACME Gateway
Automate HTTPS Without Changing Existing Systems
Deploy a dedicated hardware gateway in front of your existing Web infrastructure. Automate certificate management, HTTPS termination, supported cryptographic algorithms, and integrated security capabilities without installing ACME clients on origin servers.
Designed for enterprise environments with complex, legacy, or mission-critical infrastructure.
ACME Cloud Service
Automate Certificates Through Cloud Service
Automatically manage dual-algorithm SSL certificates by sharing cloud-deployed ACME hardware gateways or using existing CDN services.
An approach designed for cloud environments that is suitable for users who don't want to deploy a gateway locally. Also good for users who don't want to change their web server.
Why ZoTrus Focuses on the HTTPS Automation Gateway
ACME clients have already made certificate automation widely accessible. For organizations with full control over their Web servers, installing an ACME client is often a straightforward solution. CDN-based certificate automation is also available through many CDN providers.
However, enterprise infrastructure presents a different challenge. Critical business systems, legacy platforms, packaged applications, and dedicated appliances may not support ACME clients or may be difficult to modify. Upgrading every origin server to accommodate new cryptographic algorithms can also introduce operational interrupt risks and additional costs.
ZoTrus HTTPS Automation Gateway addresses this gap.
By moving public-facing HTTPS termination, certificate lifecycle management automation, and supported cryptographic agile capabilities to a dedicated gateway, ZoTrus helps enterprises modernize their website security without requiring changes to their existing origin servers or business applications. Beyond SSL certificate automation, the gateway integrates HTTPS offloading, supported hybrid post-quantum key exchange algorithms, multi-CA certificate management, and WAF protection in supported configurations.
Our focus is not to reinvent the ACME client. It is to bring automated HTTPS and evolving cryptographic capabilities to enterprise environments where conventional approaches are difficult to deploy.
One Gateway. Six Enterprise Advantages.
No Changes to Existing Web Servers
Automate HTTPS Without Modifying Your Business Systems- Deploy the HTTPS Automation Gateway in front of your existing web infrastructure.
- Automate public-facing HTTPS certificate management and encryption without installing ACME clients on origin servers or requiring application-level changes.
Five Years of SSL Certificate Automation Service
Gateway and Certificate Automation in One Solution- The gateway purchase includes five years of dual-algorithm SSL certificates up to 255 websites, combining gateway-based HTTPS automation with certificate lifecycle management for supported RSA/ECC and SM2 certificates.
- The five-year period refers to the certificate service included, not the validity period of an individual SSL certificate.
Automated Certificate Lifecycle Management
From Issuance to Renewal- Automate certificate issuance, deployment, and renewal through the gateway, reducing manual administration and the risk of missed certificate renewals.
- For RSA/ECC and SM2 certificates
Multi-CA Auto-Switching
Reduce Dependence on a Single CA- Support certificate supply through multiple CAs and automated switching mechanisms
- Helping improve resilience when an issuance channel encounters problems.
Hybrid PQC Support
Prepare Your HTTPS Infrastructure for the PQC Era- Introduce supported hybrid post-quantum cryptographic algorithms at the gateway layer, creating a practical migration path for existing web applications without requiring every origin system to implement new TLS algorithms.
- Support X25519MLKEM768 & SM2MLKEM768
Built-in WAF Protection
Combine HTTPS Automation with Web Application Security- Integrate HTTPS offloading and Web Application Firewall protection in one gateway solution
- Enabling configured web traffic inspection and protection before requests reach your origin systems.
Your Business Systems Were Not Built for Certificate Automation.
Many enterprise web applications run on legacy platforms, packaged business software, appliances, or mission- critical systems that cannot safely accommodate additional ACME clients or frequent infrastructure changes.
Manually managing SSL/TLS certificates creates another operational burden: certificates must be obtained, deployed, renewed, and replaced before they expire. At the same time, enterprises face growing pressure to prepare for post- quantum cryptography and strengthen web application protection.
Traditional solutions often address these challenges separately. Certificate automation, HTTPS offloading, PQC migration, and WAF protection can become separate projects involving different products, teams, and maintenance procedures.
ZoTrus takes a different approach: move these capabilities to a dedicated gateway in front of your existing systems.
- No ACME client installation on the origin server.
- No need to manage public-facing SSL certificates directly on the origin server.
- No need to upgrade the origin application solely to introduce gateway-supported TLS algorithms.
- A unified deployment approach for HTTPS automation, supported PQC algorithms, and WAF protection.
One Gateway Between Your Applications and the Internet (Visitor)
The gateway separates public- facing HTTPS security from the underlying business application. Existing origin systems can remain largely unchanged and offload the encryption and decryption work, letting the server resources be dedicated to the business system. Certificate private keys are generated and protected within the gateway hardware, reducing exposure associated with manual certificate handling and deployment.
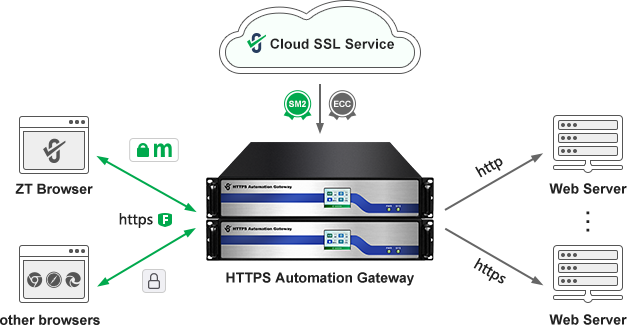
Internet & Web Clients
Browsers, customers, partners, and external applications.ZoTrus HTTPS Automation Gateway
- SSL/TLS certificate automation
- HTTPS termination and offloading
- Supported RSA/ECC/SM2/PQC algorithms
- Multi-CA certificate supply and switching
- WAF protection (traffic cleaning)
- Traffic forwarding
Existing Web Server & Business Systems
Web servers, legacy applications, and business-critical services.One Gateway, Meets the Needs of Websites of All Sizes.
ZoTrus HTTPS Automation Gateway combines certificate management, HTTPS encryption handling, and related security features into a single device. Users can choose different hardware configurations and models based on the number of websites, traffic volume, and functional requirements.


Up to 20 sites
Up to 255 sites
Up to 100 sites
Up to 200 sites
Up to 255 sites
Up to 255 sites
From Manual Certificate Operations to Automated Management
Expired certificates and manual deployments can cause unnecessary operational risks, especially when the certificates are used by multiple websites or business systems. ZoTrus HTTPS Automation Gateway integrates ACME-based certificate automation management, allowing centralized management of dual-algorithm SSL certificates, with a single gateway supporting up to 255 website systems. The gateway handles key operations like automatic certificate application, validation, issuance, deployment, and renewal, which significantly reduces repetitive manual management and greatly lowers the risk of missing renewals.

SSL certificates are applied for and deployed to web servers manually. Now, just deploy the gateway in parallel, let the website traffic flow to the gateway at the same time, and after running in parallel for a while, stop the domain resolution to the original web server's public IP. This way, smoothly switch to dual-algorithm SSL certificate automation and HTTPS automation.
Main features:
- Automated dual-algorithm SSL certificate lifecycle management
- Automated multi-algorithm adaptive HTTPS encryption
- Reduces reliance on manual certificate installation and replacement
- Centralized certificate management at the gateway layer; a single gateway can support up to 255 websites, with recommended dual-gateway hot standby and load balancing deployment
- The gateway handles HTTPS offloading externally and internal forwarding. The origin server can be reached via HTTP or HTTPS, depending on the architecture and security policy selected.
Multi-CA Certificate Supply and Switching, Reduce Dependency. Improve Operational Resilience.
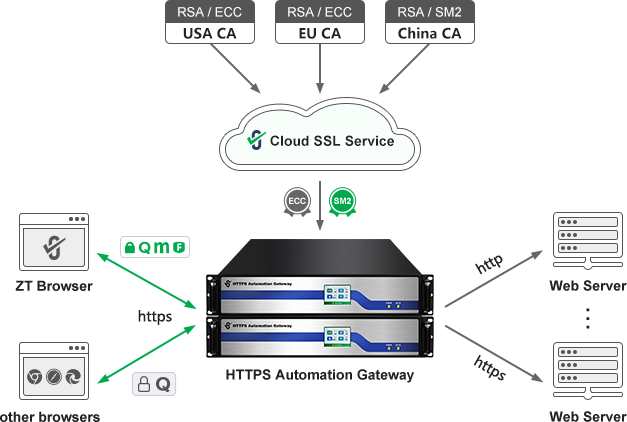
Certificate automation should not depend entirely on the availability of one CA. ZoTrus supports multiple certificate authorities and automated switching mechanisms, helping improve certificate supply resilience and reliability.
Key Benefits
- Multiple supported CA issuance channels.
- Automated selection or switching mechanisms.
- Reduced dependence on a single CA.
- A more resilient foundation for automated certificate renewal.
Post-Quantum Cryptography Migration, Without Modifying Existing Website Systems
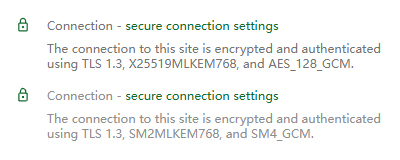
Post-quantum cryptography migration can be difficult when business applications are legacy systems, vendor-controlled platforms, or too critical to modify frequently. ZoTrus HTTPS Automation Gateway supports hybrid post-quantum cryptographic algorithms for HTTPS, including X25519MLKEM768 and SM2MLKEM768, alongside supported traditional algorithms. This allows organizations to introduce gateway-supported PQC capabilities without requiring every origin application to implement those algorithms itself.

Key Benefits
- Introduce supported PQC algorithms at the gateway layer.
- Support hybrid cryptography alongside traditional algorithms.
- Reduce the need to upgrade origin systems solely for gateway- supported TLS algorithms.
- Create a practical migration path for existing web infrastructure.
Free SM2 + PQC browser: ZT Browser
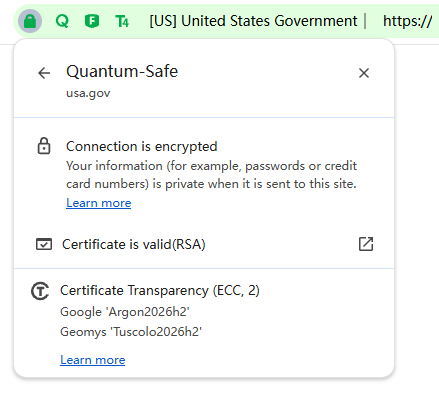
Deeply developed based on the open-source Chromium project, ZT Browser provides free support for SM2 HTTPS and post-quantum cryptography-enabled HTTPS. The prominent Q indicator in the address bar helps users easily identify HTTPS connections protected by post-quantum cryptographic algorithms, making PQC more visible and understandable and encouraging wider adoption of post-quantum cryptography.
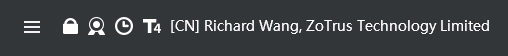
- Deeply developed based on the open-source Chromium project
- Supports SM2 SSL certificates for SM2 HTTPS encryption
- Prioritizes the hybrid PQC algorithm SM2MLKEM768 for HTTPS encryption
- Supports EV SSL certificates green address bar with organization name and T4 identity indicator
- Displays an Q indicator in the address bar to make HTTPS connections using PQC algorithms immediately recognizable
- Displays an m indicator to identify HTTPS connections using SM2 algorithm
- Allows users to click the padlock icon in the address bar to view SSL Certificate Transparency log information
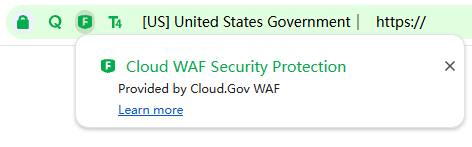
- Displays an F indicator to identify websites protected by WAF
- Includes a built-in PDF reader that verifies PDF digital signatures in real time and displays the signer's trusted identity
HTTPS Automation and Web Protection in One Gateway
ZoTrus Gateway integrated WAF capability helps inspect web traffic and apply configured protection policies before requests reach the origin server. HTTPS offloading allows the gateway to process decrypted traffic for inspection before forwarding permitted requests to the application.

Key Benefits
- Integrated WAF protection in supported configurations.
- HTTPS termination and traffic inspection at the gateway.
- Forwarding of permitted traffic to existing web applications.
- A consolidated deployment for HTTPS automation and web protection.
HTTPS Offloading and Traffic Forwarding, Let Every Security Device Do What It Does Best.
The gateway handles public- facing HTTPS encryption and decryption, reducing the need for origin servers to manage those external TLS connections directly.
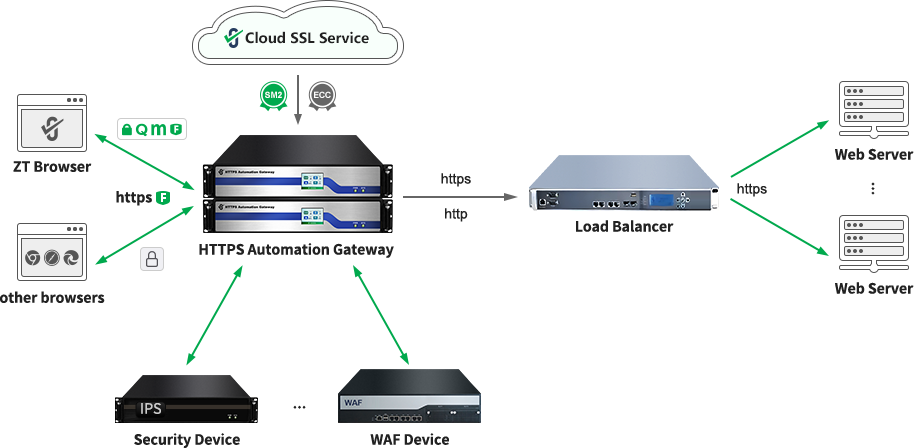
- ZoTrus HTTPS Automation Gateway centralizes SSL/TLS encryption and decryption, certificate lifecycle management, and traffic forwarding at the gateway layer. This reduces the cryptographic processing burden on downstream security devices and simplifies certificate operations without requiring changes to existing origin systems or business applications.
- Working alongside your existing firewalls, IPS, WAF, Anti-DDoS systems, and load balancers, the gateway allows each device to focus on its primary security or traffic-management role. It also helps simplify cryptographic agility as algorithms evolve toward hybrid post-quantum cryptography (PQC).
- For organizations with an existing WAF, the gateway complements rather than replaces it, helping preserve existing security investments.
- Less duplicated cryptographic work. Simpler operations. A more adaptable security architecture.
Why ZoTrus? More Than an SSL/TLS Gateway
Traditional HTTPS gateways focus primarily on TLS termination and traffic forwarding. ZoTrus combines those functions with automated certificate lifecycle management and additional security capabilities in one deployment architecture. The goal is to reduce the need to coordinate separate changes across every application.
Built for Systems That Cannot Easily Be Changed
ZoTrus HTTPS Automation Gateway is designed for organizations that need to strengthen HTTPS security while preserving existing application investments. For organizations evaluating deployment, the appropriate gateway capacity and architecture should be selected according to website count, HTTPS traffic volume, availability requirements, origin topology, and required cryptographic features.
Critical Business Infrastructure
Introduce a dedicated cryptographic application layer (HTTPS) at the network boundary instead of upgrading cryptographic features on all cybersecurity devices and keep application-level disruption to a minimum.Banking and Financial Services
Protect externally accessible business systems where application changes require careful planning, security review, and testing.Government and Public Services
Introduce automated certificate management and supported cryptographic upgrades across existing web infrastructure.Large Enterprises
Reduce the operational burden of managing certificates across multiple websites, applications, and infrastructure environments.Healthcare and Education
Improve HTTPS management and web application protection without requiring every legacy application to adopt new software.Have Questions About the ZoTrus HTTPS Automation Gateway?Find answers to common questions about deployment, certificate automation, multi- CA switching, PQC migration, WAF protection, and certificate service.
Your Existing Systems Should Not Hold Back Your Security Roadmap.
Automate SSL/TLS certificate management, introduce supported post- quantum cryptography, strengthen web application protection, and reduce single- CA dependency, with a gateway- based approach designed for existing enterprise infrastructure.
Contact ZoTrus to discuss your existing architecture, certificate management requirements, PQC migration objectives, and deployment options.